Solar Lora
[Beyond Bluetooth, WiFi, and Serial Ports] Remotely manage nodes using Meshtastic mesh networks
This article is intended for beginners who are familiar with some Meshtastic operations. Operations are risky, so please develop a good backup habit.
In addition to Bluetooth, WiFi, and serial ports, Meshtastic also supports remote node management via the mesh network. Firmware version 2.5 introduced the PKC (Public Key Cryptography) key mechanism, making remote node management very convenient. Previously, remote management could only be achieved by creating an Admin Channel.
PKC Basics
PKC (Public Key Cryptography) is the core of modern computer security systems. This article will only briefly explain it. For more information, please search: Asymmetric encryption/Public Key Cryptography
What is PKC? Let me tell you a story first
Imagine a person named Xiao Ming who lives in a digital city. He wants others to be able to send him letters, but he doesn't want others to see the secrets in the letters. So he came up with a solution:
Xiao Ming installed a special mailbox at the door of his house:
· The letter slot of this mailbox is open to everyone, and everyone can drop letters in;
· But only Xiao Ming can open this mailbox because he is the only one with the key.
This mailbox is like Xiao Ming's "public key". Anyone can use it to "send a letter" (encrypt a message), but only Xiao Ming who has the corresponding key (private key) can open it (decrypt it).
then:
· Xiaohong wants to write a letter to Xiaoming that only he can read? Just drop it in Xiaoming's mailbox!
· After receiving it, Xiao Ming uses his private key to open the mailbox and read Xiao Hong's letter, which is safe and private.
Later, Xiao Ming discovered another use for this system:
One day he sent out an important notice. He was afraid that others would say it was not written by him, so he used his own key to stamp a seal on the letter that only he could stamp.
After receiving the letter, everyone sees this special stamp and can use Xiao Ming’s mailbox (public key) to verify it and find that it is indeed Xiao Ming’s stamp. This is the “digital signature”.
As a result, Xiao Ming's "mailbox system" became a standard feature of the digital city, and everyone installed it:
· Public key = a mailbox at the door, anyone can use it;
· Private key = a key that you hide yourself and no one can see.
This is the principle of PKC: Public Key Cryptography!
In the PKC system, a person possesses a pair of keys: a public key and a private key. As the name suggests, the public key can be made public, while the private key is secret information that is never disclosed. The mathematically generated public and private keys are closely linked, and their security is guaranteed by modern cryptography. The private key is unique, and the public key can be derived from it; conversely, the private key cannot be derived from the public key.
Assume A discloses his public key:
· If you want to send a message to him secretly, you can use A's public key to encrypt it, and decrypt it only with A's private key. Since the private key is not public, only A can decrypt the message you send to him. (Encryption)
· A can use his private key to sign a message or file, proving it is his signature. Others can use A's public key to verify that the signature is from A. (Signature)
Meshtastic PKC
Meshtastic versions 2.4 and earlier will use the recipient's pre-public PSK for private chat (DM) encryption. After version 2.5, due to the addition of PKC, functions that require strong authentication will use PKC for encryption or authentication, as follows
Function | Encryption method | illustrate |
Channel Chat | PSK | Due to the public/semi-public nature of the channel, PKC group chat is not suitable |
DM private chat | PKC | Encrypted content, signed messages |
Remote Management | PKC | Verify identity and encrypt instruction content |
In the remote management part of this article, Meshtastic uses the Ed25519 elliptic curve algorithm to exchange temporarily generated PSK for communication, and also introduces Session to prevent replay attacks.
Managing remote nodes using PKC
This article takes iOS Meshtastic App as an example.
The operation is very simple. In one sentence, it is: store the public key of the control end on the controlled end.
Control terminal
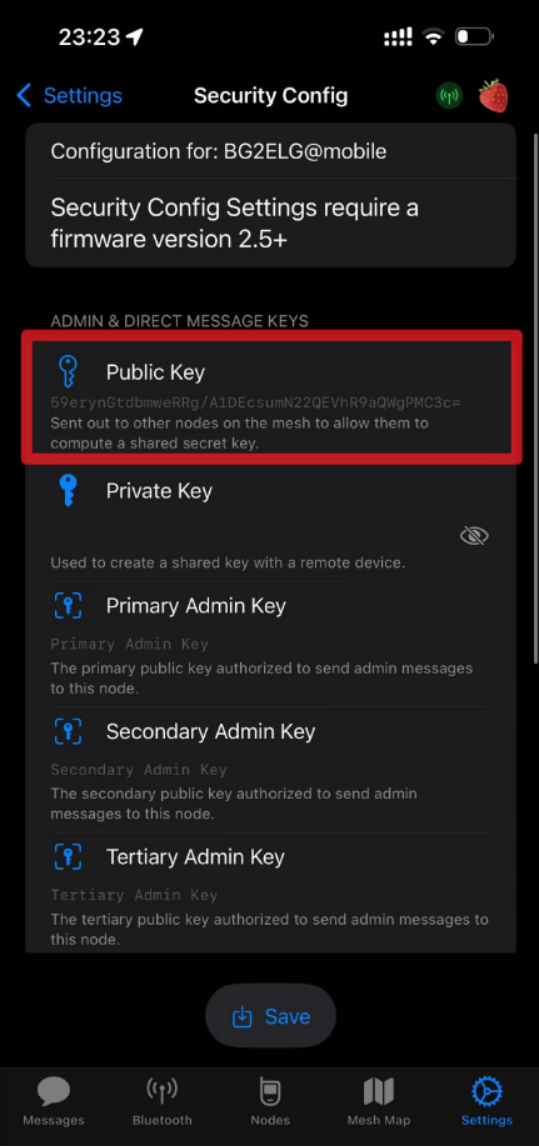
Go to Settings ➡️ Security, long press and copy the Public Key.
controlled end
Go to Settings ➡️ Security, paste the copied Public Key into Primary Admin Key, and save.
There are three slots (Primary, Secondary, and Tertiary) that can accept control from up to three nodes.
Remote Control
On the control side, open Settings ➡️ App Settings, turn on Administration, and then return to the previous level Settings directory.
At this time, there will be an additional list for selecting nodes, and you can select the controlled end here.
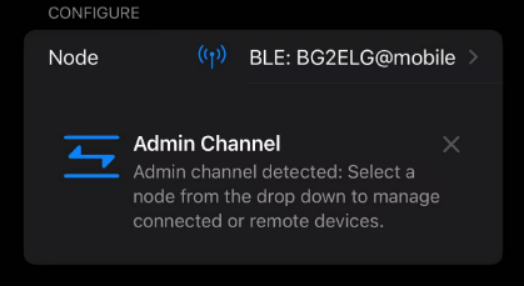
The software will negotiate when the connection is started, and the node name will turn into small characters after remote control is ready.

The nodes can then be managed through the Mesh network.
Author: Qiqihar-BG2ELG | Community Group Member
Translator:Joe Tan | KEEPTEEN | meshtastic node repeater
Website: https//www.keepteen.com
0users like this.


 Cart